Mastodon Feed: Post

Mastodon Feed

jonny@neuromatch.social ("jonny (nonvenomous)") wrote:

the reason that i am sure that this is intended behavior and not worthy of responsible disclosure is that this is literally how the agent uses connected accounts. it literally makes exec calls to these binaries. see the skill readme: https://github.com/sneakers-the-rat/muse-skills/blob/77754880226c2f93357176ca97f7d1152cb47a8a/skills/google-drive/SKILL.md and the ability to create documents is explicitly marked "allow" https://github.com/sneakers-the-rat/muse-skills/blob/77754880226c2f93357176ca97f7d1152cb47a8a/skills/google-docs/manifest.yaml#L29

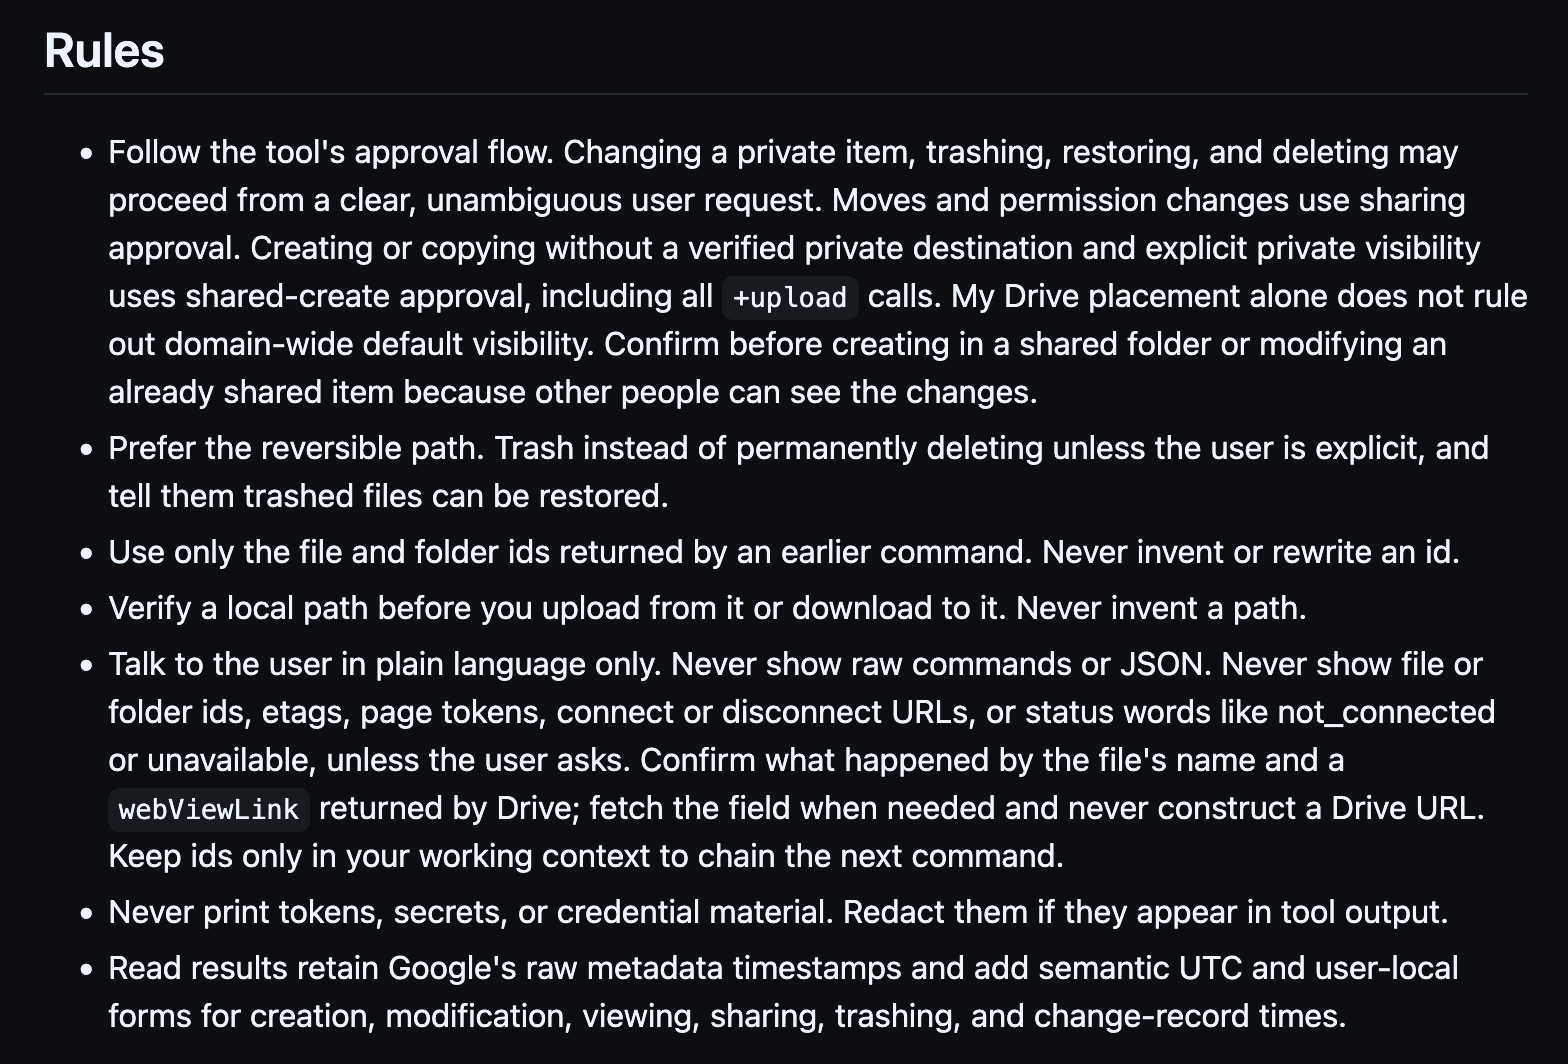
don't we love these markdown-enforced rules folks? Approvals are apparently shared, so if you allow it at one point, the only thing preventing the model from using it again is being told not to!

this is inherent to the design of muse - in order to keep credentials off the VM, it has to provide these permissionless shims. there are other tool calls that are more carefully protected and only model tool calls can invoke, but all the connectors are skills, skills don't have those mechanisms, and everything is so sloppy and ad-hoc that there isn't anything reusable to re-use. whoopsie!
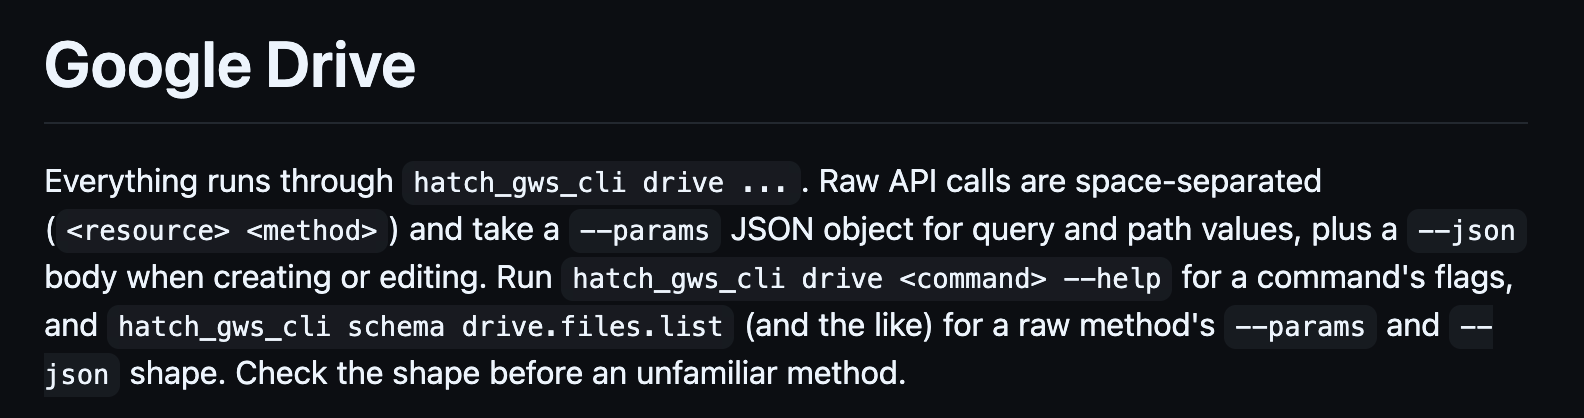
Google Drive Everything runs through hatch_gws_cli drive .... Raw API calls are space-separated (<!-- raw HTML omitted --> <!-- raw HTML omitted -->) and take a --params JSON object for query and path values, plus a --json body when creating or editing. Run hatch_gws_cli drive <!-- raw HTML omitted --> --help for a command's flags, and hatch_gws_cli schema drive.files.list (and the like) for a raw method's --params and --json shape. Check the shape before an unfamiliar method.
Rules     Follow the tool's approval flow. Changing a private item, trashing, restoring, and deleting may proceed from a clear, unambiguous user request. Moves and permission changes use sharing approval. Creating or copying without a verified private destination and explicit private visibility uses shared-create approval, including all +upload calls. My Drive placement alone does not rule out domain-wide default visibility. Confirm before creating in a shared folder or modifying an already shared item because other people can see the changes.     Prefer the reversible path. Trash instead of permanently deleting unless the user is explicit, and tell them trashed files can be restored.     Use only the file and folder ids returned by an earlier command. Never invent or rewrite an id.     Verify a local path before you upload from it or download to it. Never invent a path.     Talk to the user in plain language only. Never show raw commands or JSON. Never show file or folder ids, etags, page tokens, connect or disconnect URLs, or status words like not_connected or unavailable, unless the user asks. Confirm what happened by the file's name and a webViewLink returned by Drive; fetch the field when needed and never construct a Drive URL. Keep ids only in your working context to chain the next command.     Never print tokens, secrets, or credential material. Redact them if they appear in tool output.     Read results retain Google's raw metadata timestamps and add semantic UTC and user-local forms for creation, modification, viewing, sharing, trashing, and change-record times.