Mastodon Feed

Boosted by soatok@furry.engineer ("Soatok Dreamseeker"):
danluu ("Dan Luu") wrote:
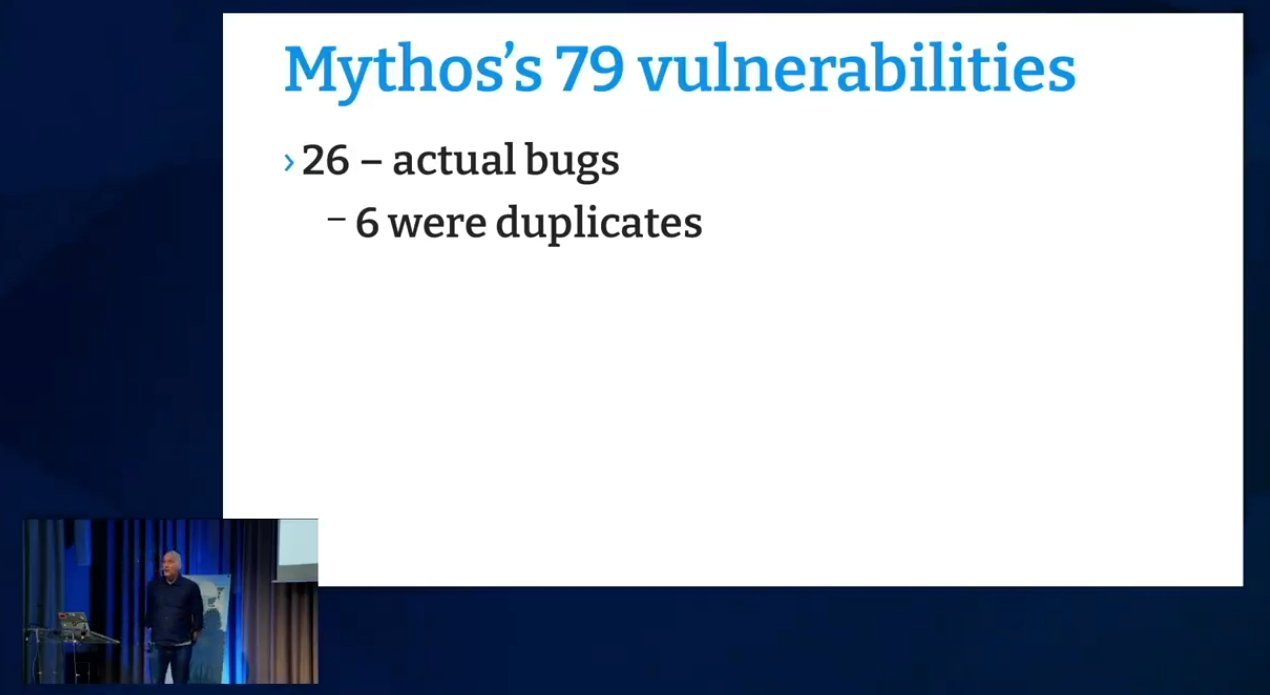
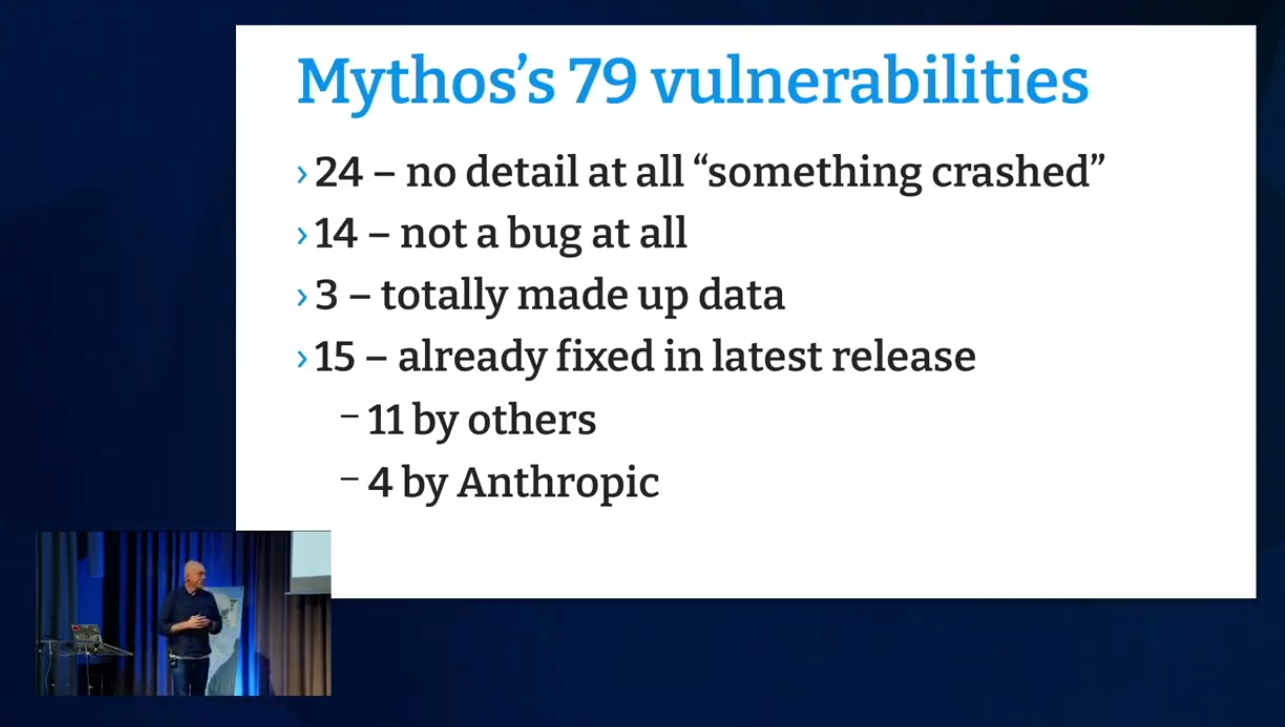
Why didn't Anthropic do effective false positive rejection with their Mythos/Glasswing vuln reports? In https://danluu.com/ai-coding/#mythos, I mentioned a colleague finding that the reports we got were mostly nonsense.
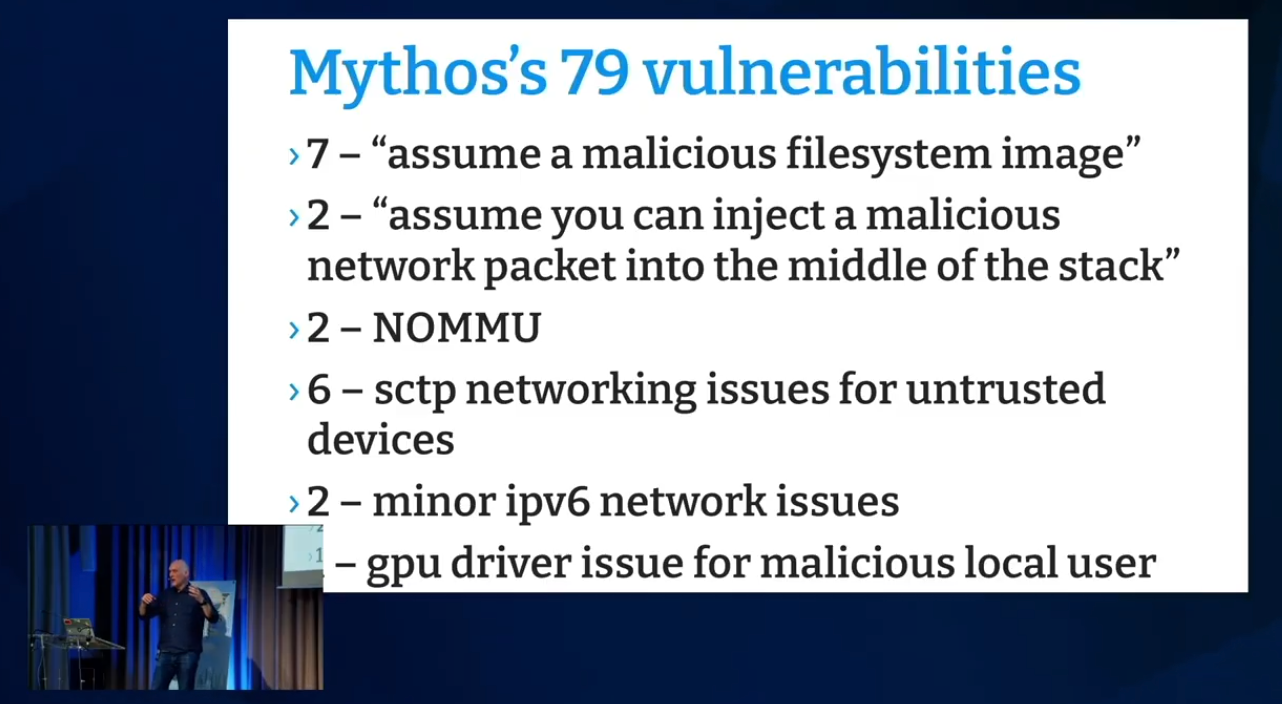
At the time, I wondered our reports were particularly bad, but as more people talk about their experiences, getting mostly nonsense reports seems to have been common? E.g., here's @gregkh on Linux kernel reports (h/t @KernelRecipes); see also https://www.vulncheck.com/blog/anthropic-glasswing-receipts.
![] »7 — “assume a malicious filesystem image” »2 - “assume you can inject a malicious network packet into the middle of the stack” »2-NOMMU » 6 — sctp networking issues for untrusted devices »2 — minor ipv6 network issues HL : — gpu driver issue for malicious local user diy ]7