Mastodon Feed: Post

Mastodon Feed

brennan@social.lol ("Brennan Kenneth Brown") wrote:

My case was escalated with Apple Support, and there was absolutely nothing server-side on their end that indicated the wipe. (MDM was also ruled out)

Regarding backups and data, I'm fine as all of my work is on git and my homelabs, only the *how* of what happened is my concern.

If my device was compromised, it was compromised in a way that seems undetectable.
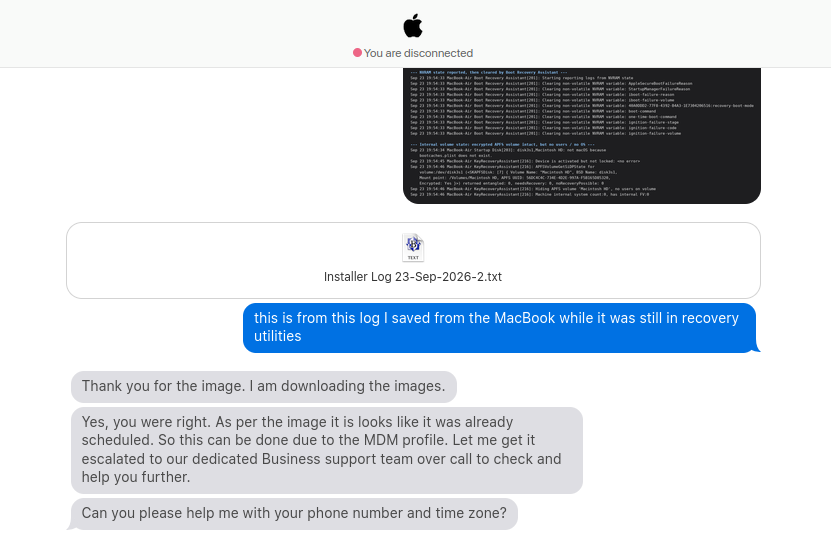
Screenshot of a chat support conversation styled with an Apple logo at the top and a red status dot reading 'You are disconnected.' Below the header is a dark terminal-style log panel showing MacBook Air recovery/boot messages, including entries about NVRAM state, RTC panic info, clearing non-volatile RAM variables (AppleFirmwareFailureReason, StartupMuteReason, boot-failure-reason, etc.), an internal volume status showing an encrypted APFS volume as 'Intact, but no users' on disk0, and MacRecoveryAssistant log lines referencing a locked device, a volume named 'Macintosh HD', and machine internet connection checks. Below the log image is an attached text file labeled 'Installer Log 23-Sep-2026-2.txt' with a document icon. Under it, a blue chat bubble from the user reads 'this is from this log I saved from the MacBook while it was still in recovery utilities.' Below that are three gray support-agent chat bubbles: one saying 'Thank you for the image. I am downloading the images.', another saying 'Yes, you were right. As per the image it looks like it was already scheduled. So this can be done due to the MDM profile. Let me get it escalated to our dedicated Business support team over call to check and help you further.', and a final one asking 'Can you please help me with your phone number and time zone?'